Giving every team member full access to a customer relationship management (CRM) system may seem convenient, especially when a small business relies on employees and contractors to handle multiple responsibilities. However, unrestricted access creates opportunities for accidental data changes, unauthorized exports, and uncertainty over who is responsible for customer information.
The issue is not whether employees should be trusted. It is whether their access matches the work they actually need to perform. A defined CRM permission structure helps protect customer records while allowing teams to work efficiently.
Why CRM Permission Problems Develop as Businesses Grow
Many businesses establish their CRM permissions during initial setup and rarely revisit them.
The owner creates an administrator account, invites employees, and assigns broad access to avoid interruptions. As responsibilities change, those original permissions often remain in place.
Eventually, team members may have access to records, settings, or export functions unrelated to their current responsibilities.
Convenience Often Replaces Access Planning
When permissions are unclear, businesses may grant additional access whenever someone encounters a restriction.
The immediate problem disappears, but the account now has more authority than the role requires.
Applying this principle to CRM management means assigning permissions according to responsibilities rather than convenience.
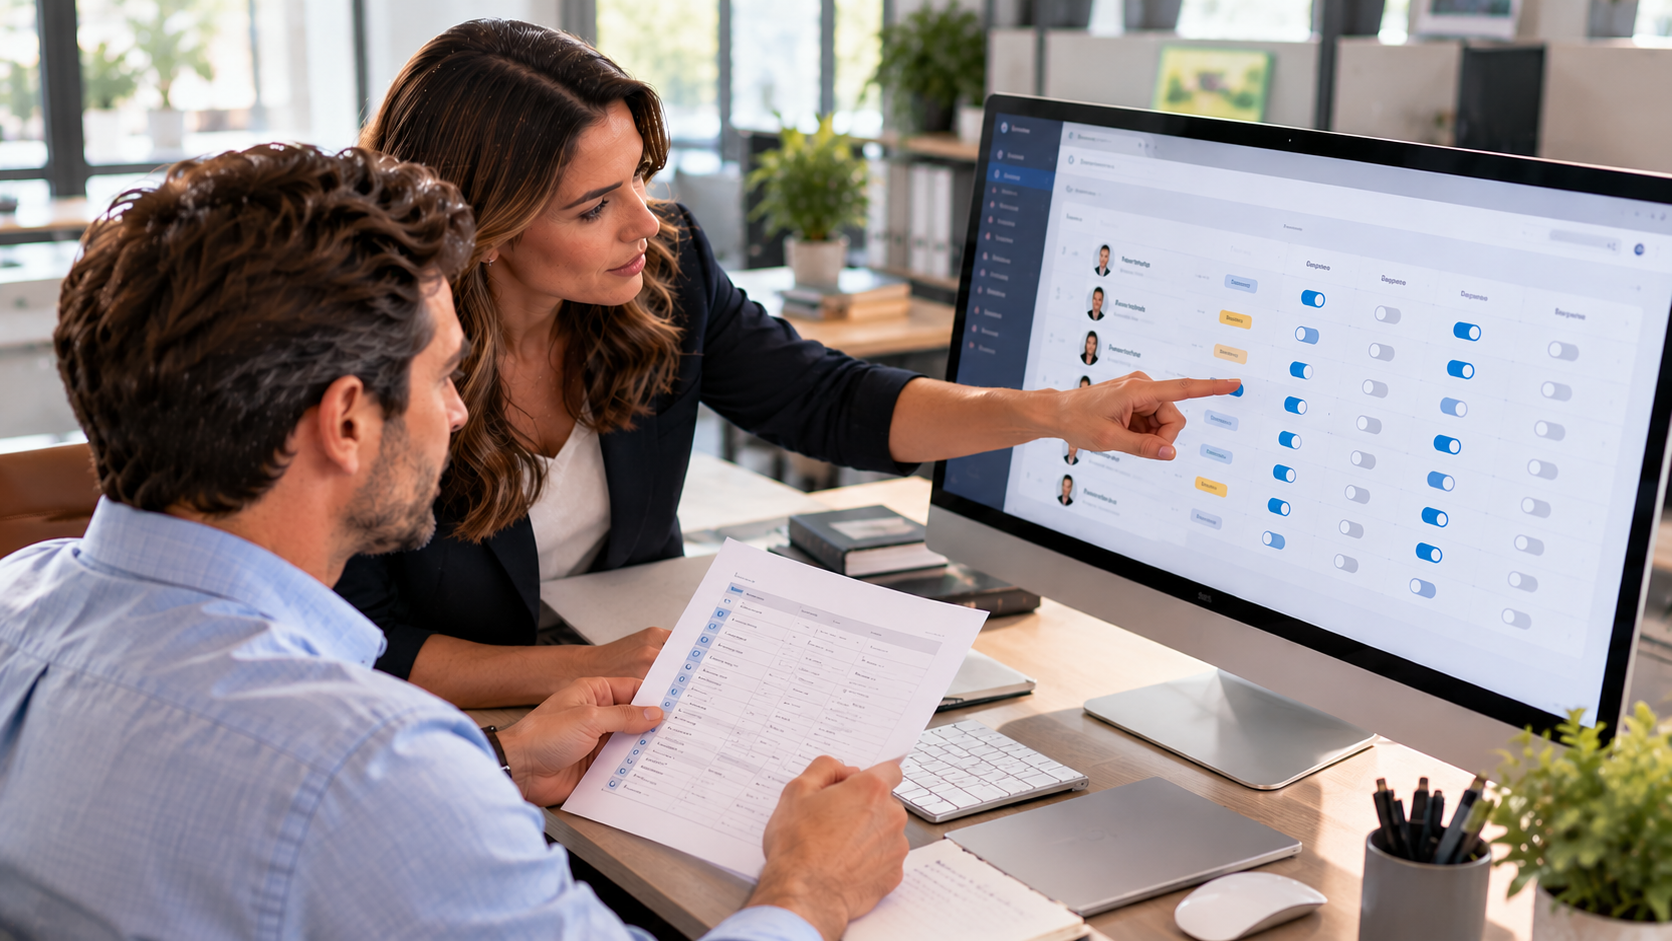
Who Should Be Allowed to View, Edit, Delete, or Export CRM Records?
CRM permissions should reflect the decisions and responsibilities associated with each role.
The Federal Trade Commission recommends restricting sensitive customer information to employees and contractors who need it to perform their work.
1. Business Owners and CRM Administrators
Owners typically need oversight of customer information, system configuration, and permission assignments.
A designated CRM administrator may need broader access to manage workflows, integrations, duplicate records, and user accounts.
However, administrator access should not automatically extend to every employee with management responsibilities.
2. Sales Teams and Client-Facing Employees
Sales representatives generally need to view and update customer records related to their assigned accounts.
This may include contact information, communication notes, pipeline stages, and follow-up activities.
They do not necessarily need permission to delete entire customer lists, change system-wide settings, or export the complete database.
3. Virtual Assistants and Administrative Support
Virtual assistants often need CRM access to maintain accurate customer records, organize leads, update contact information, and monitor follow-up workflows.
Their permissions should be based on the services they provide.
4. External Contractors
Marketing agencies, consultants, and technical providers may require temporary access to complete specific projects.
Businesses should limit access to the relevant records and remove permissions when the engagement ends.
How to Maintain CRM Permissions Over Time
Permission settings should not remain unchanged after initial configuration.
Employees change roles, contractors complete projects, and businesses introduce new CRM integrations.
NIST's Cybersecurity Framework 2.0 emphasizes managing identities, credentials, and access permissions according to organizational risk.
Create a Regular Access Review Process
A quarterly review is a practical starting schedule for many small businesses, with immediate reviews when someone joins, changes responsibilities, or leaves.
The review should confirm that:
Every active account belongs to an authorized user.
Permissions match current responsibilities.
Export and deletion privileges remain justified.
Former employees and contractors no longer have access.
Shared accounts are replaced with individual accounts where possible.
Multifactor authentication is enabled where supported.
The business should also document who approves permission changes and how those changes are recorded.
Protect Customer Records Without Slowing Down Your Team
Effective CRM access control is not about restricting employees unnecessarily. It is about giving each person the permissions required to perform their responsibilities without exposing unrelated customer information.
When businesses separate viewing, editing, deleting, and exporting privileges, they reduce avoidable risks and create clearer accountability.
With documented procedures, periodic reviews, and reliable virtual assistant support, CRM management becomes more consistent as the business grows.


Leave a Reply